Scheduled maintenance on internal systems used for Customer Support interactions will take place on Friday, 13 November 2026 at 4:00 PM PST through Sunday, 15 November 2026 at 2:00 PM PST (Saturday, 14 November 2026 at 00:00 UTC through Sunday, 15 November 2026 at 22:00 UTC).
Customer Support will be unavailable during this window, with normal operations resuming immediately following the completion of the work. Responses to requests submitted during the downtime will experience delays, and this status page will be updated once the maintenance concludes. For urgent support inquiries please reach out to your Procore Point of Contact.
Welcome to our new support center!
Here, you will find answers to all your questions about Procore products and features—more easily than ever before. This is now the only support site for Procore. The previous site (support.procore.com) is now obsolete and will no longer be updated.
Configure SP-Initiated SSO for Procore in OneLogin
Note
If your organization is using the Portfolio Financials and Capital Planning products in Procore, you will need to reach out to your Procore point of contact or the Support team to set up your OneLogin SSO.
Background
Term
SP-Initiated Context
IdP-Initiated Context
Identity Provider (IdP)
Authenticates the user after receiving a request from Procore.
Authenticates the user directly within the IdP portal and initiates the session.
Service Provider (SP)
Procore—initiates the login request and consumes the returned assertion.
Procore—receives and validates the unsolicited assertion from the IdP.
Issuer URL (Entity ID)
Identifies Procore as the entity requesting authentication.
Identifies your IdP as the entity issuing the authentication assertion.
Target URL
The IdP endpoint where Procore sends the SAML AuthnRequest.
The IdP app tile/launch URL that routes the user directly to Procore.
SAML
Protocol used to pass requests to the IdP and assertions back to Procore.
Protocol used to push pre-generated authentication assertions directly to Procore.
X.509 Certificate
Verifies signatures on both outgoing requests and incoming assertions.
Verifies the IdP's digital signature on the incoming authentication assertion.
If your company wants to configure Single Sign-On with OneLogin, you can leverage one of Procore's supported SSO solutions:
Identity Provider Initiated (IdP-initiated) SSO. With this option, your end users must log into your Identity Provider's SSO page (e.g., OneLogin) and then click an icon to log into and open the Procore web application. To configure this solution, see Configure IdP-Initiated SSO for OneLogin. OR
Service Provider Initiated (SP-initiated) SSO. Referred to as Procore-initiated SSO, this option gives your end users the ability to sign into the Procore Login page and then sends an authorization request to the IdP. Once the IdP authenticates the user's identify, the user is logged into Procore. To configure this solution, see the Steps below.
Things to Consider
Required Permissions:
Administrator permission to OneLogin. AND
'Admin' level permissions to Procore's Company level Admin tool.
Prerequisites:
Ensure that you have added your Procore users to OneLogin, For step-by-step instructions, please visit the OneLogin Help Center.
Procore-initiated SSO supports both single domain and multiple domain sign in. After completing the steps below, you must provide your SSO domain(s) to your company's Procore point of contact. This information will added to Procore as a final configuration step before you test your SSO configuration.
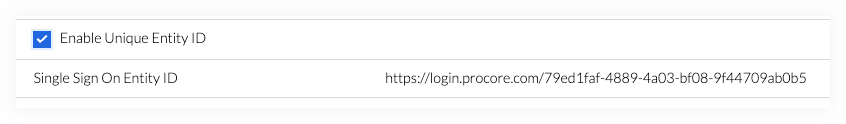
Tip: When to use 'Enable Unique Entity ID' in Procore
Single Instance: If your company only manages one (1) Procore company instance, clear the Enable Unique Entity ID check box.
Multiple Instances: If your company manages multiple Procore company instances and requires a dedicated enterprise application for each instance in your IdP, mark the Enable Unique Entity ID check box. Note that each Procore instance is still limited to one (1) enterprise application.
Important Requirements & Limitations:
Email Domain Rule: Procore targets SSO users by email domain. An email domain can only be mapped to one (1) Procore company instance across the entire platform.
Generating the URL: You must select the EnableUnique Entity ID check box on the SSO Configuration page in the Company Admin tool before the unique Single Sign On Entity ID URL will appear in Procore (the service provider). Once generated, copy and paste this URL into the IdP's Entity ID field.
Access & Provisioning: Enabling this check box does not alter company access. Access to a company instance in Procore is determined by a user's presence in the company's Directory tool and their configured tool permissions. Automated user provisioning is not currently supported.
Steps
Complete these steps:
Step 1: Add the Procore App to OneLogin
Step 2: Configure Procore-Initiated SSO for OneLogin
Step 3: Add the OneLogin Settings to Procore's Company Admin Tool
Step 1: Add the Procore App to OneLogin
Log in to your organization's OneLogin portal as an Administrator.
Choose Apps > Add Apps. This reveals the Find Applications page.
At the Find Applications page, type: Procore The Procore app will appear.
Click the Procore app. This reveals the Configuration page.
Verify the following:
Display Name. Verify that the entry reads "Procore".
Visible in Portal. A GREEN checkmark should appear.
Rectangular Icon. The Procore logo should appear.
Square Icon. The Procore icon should appear.
Description. This is not a required field. Enter data only if you want to.
At the top-right, click Save. A green banner appears to confirm that the app was successfully added.
Step 2: Configure Procore with the SSO Settings from OneLogin
In the new app's page in OneLogin, click the SSO tab. This tab provides you with access to all of OneLogin's SSO Settings. Later, you will add the settings that you copy on this page to Procore's Company Admin tool.
In the X.509 Certificate box, click View Details. This opens a page showing all the certificate details.
In the top-right corner of the X.509 Certificate box, click Copy to Clipboard. This copies the X.509 certificate to your web browser's clipboard. Important! When using the OneLogin website, you might want to paste the items you copy into a Notepad document, to ensure that the Copy to Clipboard command worked as expected. When the copy command is successful, the browser will display a 'Copied' tooltip like the one illustrated below. If the copy command does NOT work in your browser version, simply place your mouse cursor in the text field the copy all the text (e.g., press CTRL+C in Windows or CMD+C on a Mac).
Paste the X.509 certificate that you copied into the X.509 Cert field.
Click the Format X.509 Certificate button. The OneLogin tool automatically formats the certificate in two ways -- with the header or with the string.
Scroll to X.509 Cert in String Format box at the bottom of the page. Then choose one of the options to copy the certificate information:
Click the Copy to Clipboard icon in the top-right corner of the X.509 Cert In String Format box. OR
Select all of the text in the X.509 Cert In String Format box. Then right-click and choose Copy from the shortcut menu.
Leave the Format an X509 Certificate page open. You will need to copy some information in this page when performing next configuration step in the Procore for web application.
Step 3: Add the OneLogin Settings to Procore's Company Level Admin Tool
Leave the Format an X509 Certificate page page open as described in the previous step.
Under Administrative Settings, click Single Sign On Configuration.
Paste the information from OneLogin into Procore as follows:
In Procore, scroll to the bottom of the page and click Save Changes. This saves your SSO configuration.
Next, reach out to your company's Procore point of contact or contact Procore Support to request that they enter the domains you want to target for authentication via SSO. Procore must enter these domains on your behalf.
Once the domain(s) have been entered by Procore, take the final steps to enable SSO for your company:
Mark the Enable Single Sign On box in Procore's SSO configuration settings.
Select Service Provider Forward to enable an SP-initiated flow.
Click Save.
Authentication via the configured SSO method will become active immediately after saving the final completed configuration.