Configure Google SSO for Procore
Note
If your organization is using the Portfolio Financials and Capital Planning products in Procore, you will need to reach out to your Procore point of contact or the Support team to set up your SSO.
If your organization is using the Portfolio Financials and Capital Planning products in Procore, you will need to reach out to your Procore point of contact or the Support team to set up your SSO.
If your company wants to configure Single Sign-On with Google SSO, you can leverage this solution:
Service Provider Initiated (SP-initiated) SSO. Sign into the Procore Login page and use Google SSO for identity management.
Required User Permissions:
Super admin (or super administrator) to Google
'Admin' level permissions on the Company level Admin tool
Supported Authentication Protocol:
Security Assertion Markup Language (SAML 2.0)
Additional Information:
Limitations:
Just In Time (JIT) provisioning is NOT supported.
See Google's Set up your own custom SAML application for more information on the steps below.
Navigate to the Google Identity Provider details page in Google's Admin console.
Open a blank document on your computer.
Copy the SSO URL from the Google Identity Provider details page and paste it into your blank document.
Copy the Entity ID from the Google Identity Provider details page and paste it into your blank document.
Download the Certificate from the Google Identity Provider details page.
Open the Certificate and copy the text between Begin Certificate and End Certificate.
Paste the Certificate text into your blank document.
Complete the following in Google's Service Provider Details window:
Entity ID: https://login.procore.com/
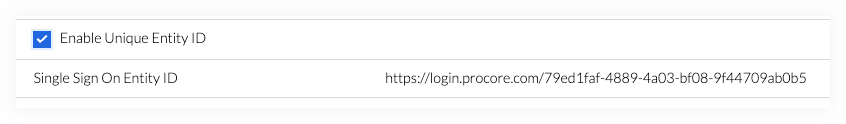
Single Instance: If your company only manages one (1) Procore company instance, clear the Enable Unique Entity ID check box.
Multiple Instances: If your company manages multiple Procore company instances and requires a dedicated enterprise application for each instance in your IdP, mark the Enable Unique Entity ID check box. Note that each Procore instance is still limited to one (1) enterprise application.
Important Requirements & Limitations:
Email Domain Rule: Procore targets SSO users by email domain. An email domain can only be mapped to one (1) Procore company instance across the entire platform.
Generating the URL: You must select the Enable Unique Entity ID check box on the SSO Configuration page in the Company Admin tool before the unique Single Sign On Entity ID URL will appear in Procore (the service provider). Once generated, copy and paste this URL into the IdP's Entity ID field.
Access & Provisioning: Enabling this check box does not alter company access. Access to a company instance in Procore is determined by a user's presence in the company's Directory tool and their configured tool permissions. Automated user provisioning is not currently supported.
Start URL: Leave this field blank.
Certificate: Copy and paste the Certificate text from your blank document.
Signed Response: Mark this checkbox.
Name ID: Select Basic Information in the first drop-down menu and Primary Email in the second drop-down menu.
Name ID Format: Select EMAIL in the drop-down menu.
Navigate to the Company level Admin tool in Procore.
Under Company Settings, click Single Sign On Configuration.
Complete the following:
Enter the Entity ID from the Google Identity Provider details page in the Single Sign On Issuer URL field.
Enter the SSO URL from the Google Identity Provider details page in the Single Sign On Target URL field.
Enter the Certificate text in the Single Sign On x509 Certificate field.
Click Save Changes.
Reach out to Procore Support or your company's Procore point of contact to request to enable SSO. Include the email domain you'd like to target for SSO in your request.
After you receive confirmation that the SSO configuration is ready, mark the Enable Single Sign On checkbox on the 'Single Sign On Configuration' page.
Do one of the following:
Select the Allow Password Login option.
Select the Service Provider Forward option.
Click Save Changes.
Loading related articles...